Update, October 2026: Microsoft renamed Azure Sentinel to Microsoft Sentinel in 2021. The ideas here still hold: KQL analytics, Logic Apps playbooks, workbooks, and threat hunting. Some screens, feature names, and where you manage the product have changed since 2020. Microsoft's Sentinel overview describes the current product.
Today, we hear new buzzwords every day, especially in the IT world. Cybersecurity isn’t immune to this, considering how fast things are changing these days.
If you haven’t heard about SOAR yet, let me introduce you to the latest and greatest in automated cybersecurity. SOAR stands for Security Orchestration, Automation and Response. This, thankfully, isn’t just a buzzword. It’s the next step in the direction towards proactive, responsive, intelligent and automated cybersecurity.
More details on SOAR from this InfoSec Institute blog.
That’s a lot of adjectives you might say, but they all apply provided you pick the right tool.
The days of hackers manually trying every known trick in their books are gone. Vulnerabilities are bought and sold in the dark web, along with credentials and the tools to exploit these. The bad guys, I am afraid, always try to stay one step ahead. They use automated tools to run hundreds of thousands of scans, attacks, and reconnaissance using the power of the cloud. And it’s not just the lone hackers you need to be worried about. State actors are increasingly targeting both public and private organizations to gain an edge over each other.
Add AI (Artificial Intelligence) and ML (Machine Learning) to the mix, and you really have to ask yourself whether you are still relying on cybersecurity tools that are not proactive, responsive, intelligent and automated.
This is where Microsoft’s Azure Sentinel comes in. It’s a cloud native smart SIEM (Security Information and Event Management) solution which combines the power of the Cloud, Microsoft’s immense ever-increasing knowledge of security threats (Microsoft Intelligent Security Graph) and Logic Apps (no code drag and drop functions) to provide a SOAR solution that harnesses the power of analytics, AI and ML to automate your cybersecurity.
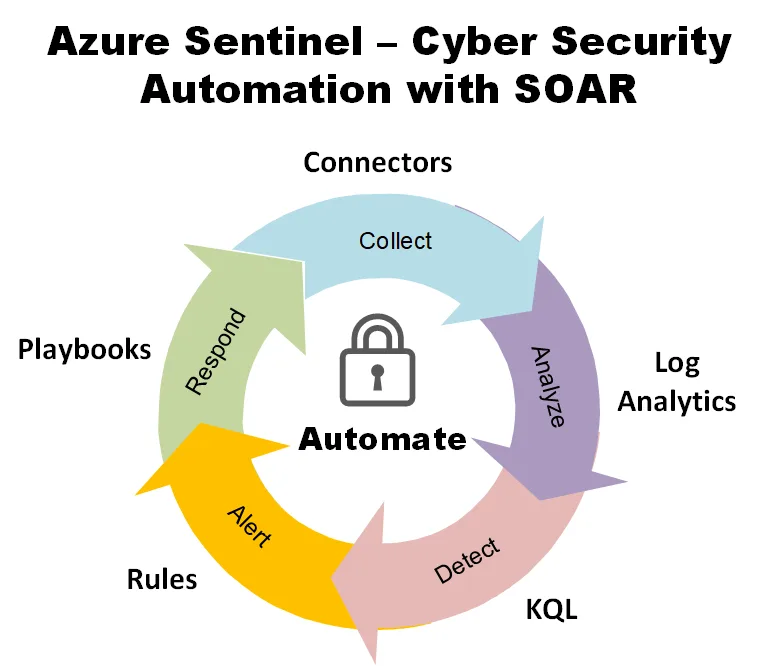
Cybersecurity Automation with Azure Sentinel
Here’s a list of things you get with Azure Sentinel:
Workbooks – Generate awesome interactive reports in real time with the ability to export these to CSVs or even Power BI if you wish
Playbooks – No/low code drag and drop Logic Apps which help you react to any security alerts or incidents in real time. You even have 200+ connectors to work with other tools like email providers, ITSM services, or plain old web hooks.
Analytics – Sentinel uses Azure Monitor at the back, so you can run increasingly powerful queries to correlate data from across your organization using KQL (Kusto Query Language)
Threat hunting – based on the MITRE framework
Investigate - Guided help with Azure AI and Intelligent Security Graph to investigate security incidents.
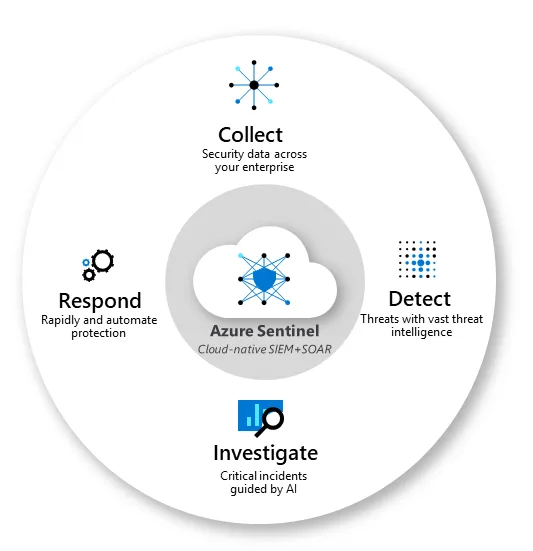
Azure Sentinel Features
In my opinion, the last one is the biggest benefit because Microsoft provides the ability to ingest security data from many security providers, and considering its reach, you have a higher chance of being protected from those pesky zero-day vulnerabilities. The system learns from one tenant and recognizes the same pattern being executed in another, alerting you and potentially stopping it in its tracks.
You have access to hundreds of templates and ready-built solutions in all areas of the solution ready to choose from. And if that doesn’t meet your needs, the Microsoft Sentinel GitHub community has even more.
Last but not least, Microsoft listens: its engineers take part in the Microsoft Sentinel tech community.
We like what we do here at Zephon, and we are staunch believers in cybersecurity education, so if you have questions about how Microsoft Sentinel can help you, reach out to us.